Navigate the Console
The Console is the central control panel for Tenable. The Console provides a comprehensive interface for managing and assessing the security posture of your entire cloud environment. This article guides you through the primary navigation elements to help you find what you need.
Left-Hand Navigation Menu
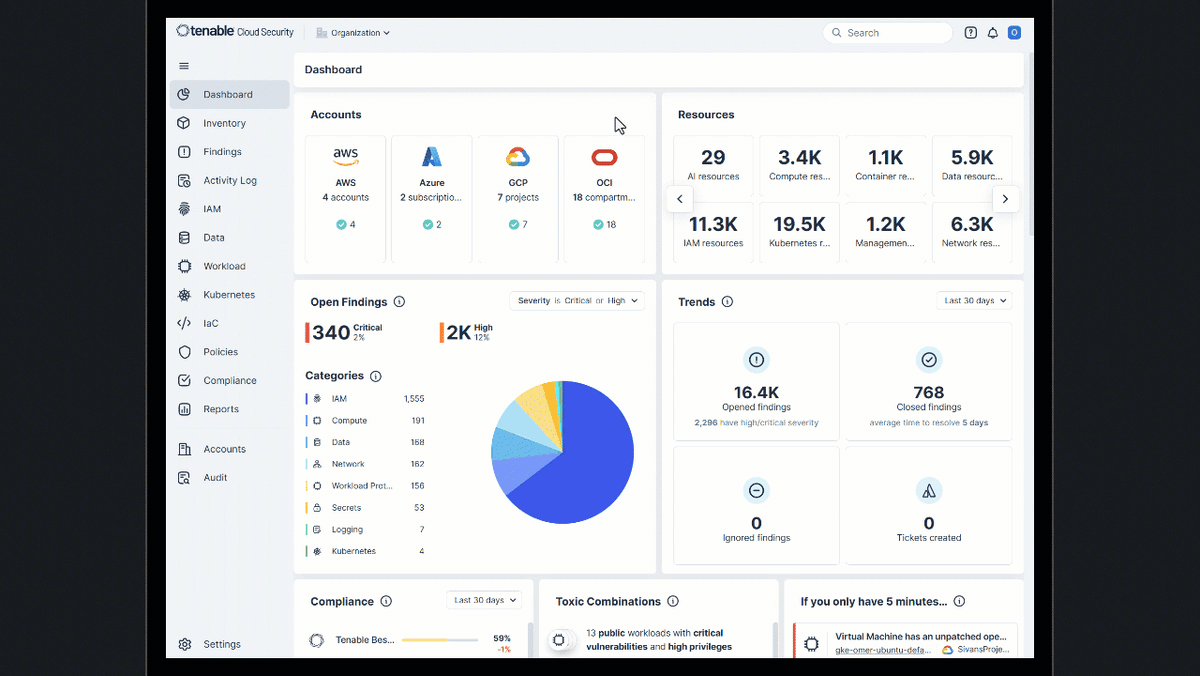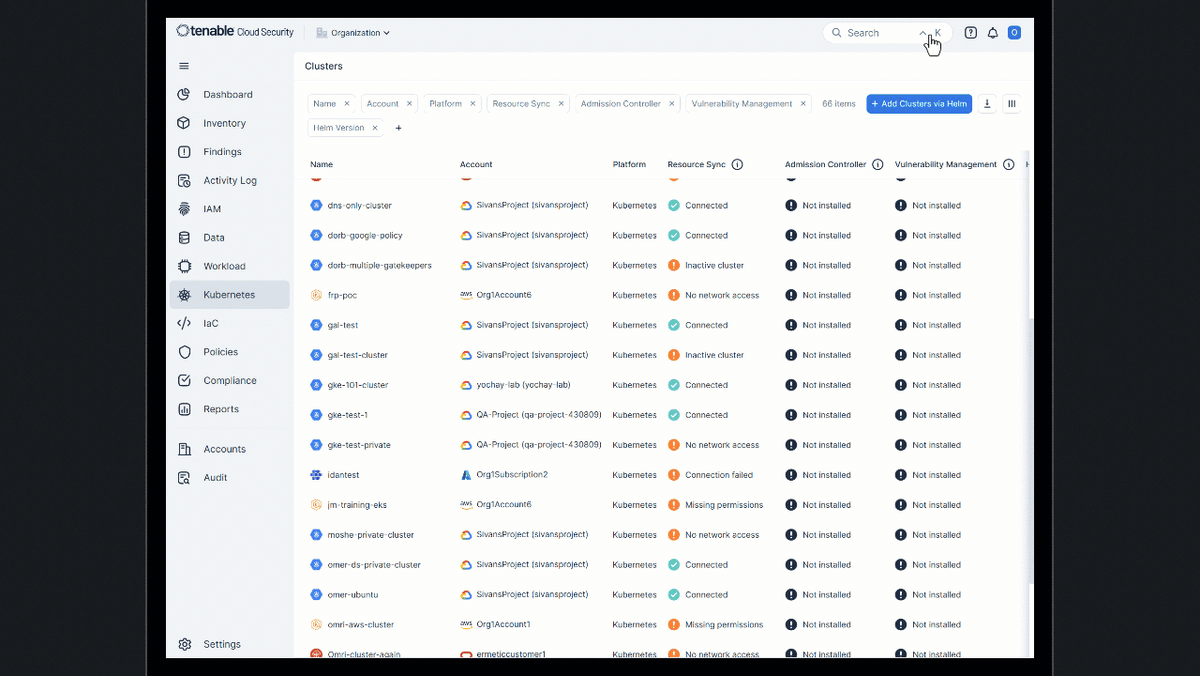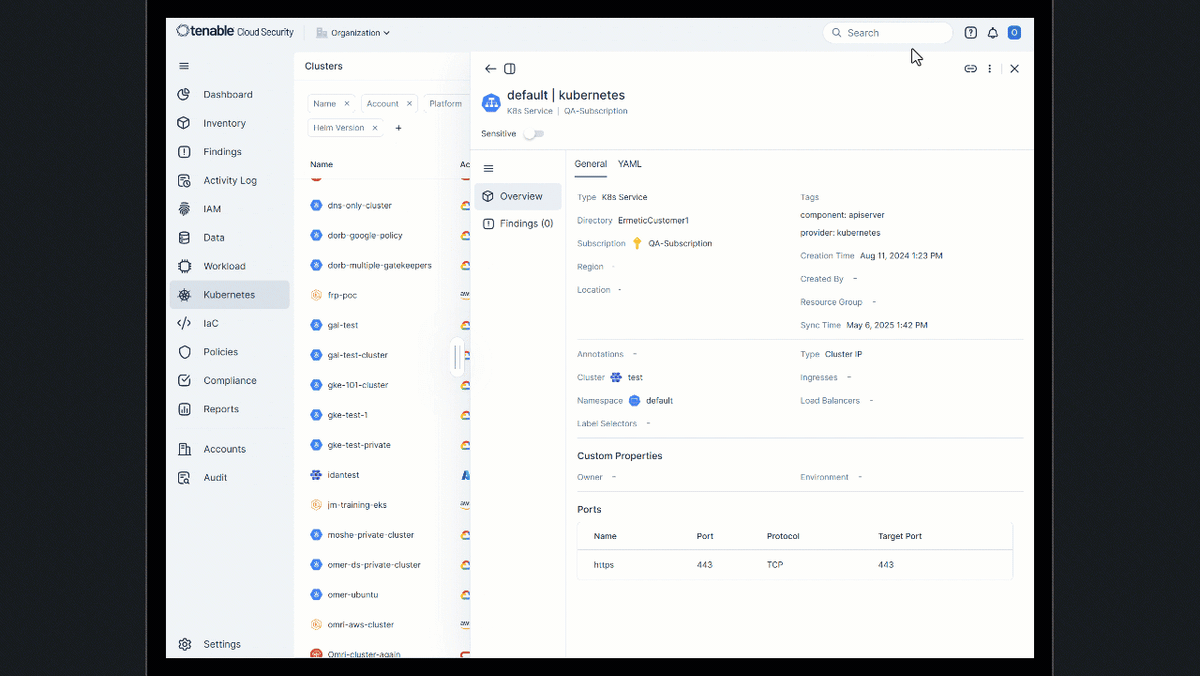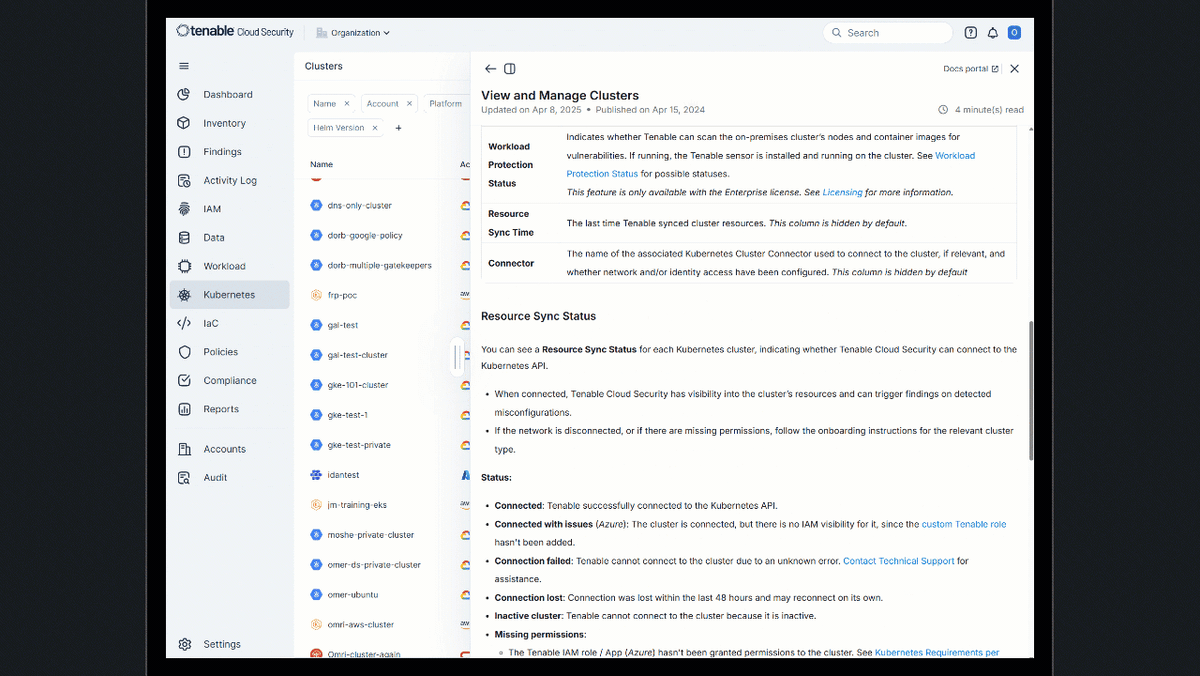
When you log into the Console, the Dashboard page appears. From here, you can investigate potential risks in your environment via Dashboard widgets, or use the left-hand navigation menu to go to relevant areas of the product.
If you're an Administrator user, you will also see the Settings menu.
| Menu Item | Description |
|---|---|
| Dashboards | Comprehensive overview of your cloud environment, giving you a snapshot of your asset count and security posture. |
| Explore | Centralized asset view of all cloud resources identified by Tenable One Cloud Exposure, along with additional tools to analyze and investigate security data, query permissions, review activity logs, and identify anomalous behavior. |
| Risks | Assess and prioritize security risks, including findings, excessive permissions, vulnerabilities, and CI/CD scans. |
| Policies | Define and enforce automated guardrails for identities, resources and network configuration, preventing unauthorized access to your cloud environment. |
| Operations | Create automation rules that integrate with and send Cloud Exposure data to third-party tools. |
| Reports | Create high-level reports for asset inventory, misconfigurations, summary, and compliance information. Ensure compliance with common industry standards and security best practices. |
Select Your Console Focus
You can personalize your Console view to highlight the features that are most important to you. Setting a Focus tailors your experience by filtering the visible menu items, dashboard widgets, and reports to information relevant to your chosen domain, reducing complexity and increasing efficiency.
For example, if you’re responsible for data protection, you can set your Focus to Data Security so the Console shows only findings, dashboards, and reports related to sensitive data exposure. This keeps you from sorting through unrelated vulnerabilities or access issues and lets you zero in on what matters most to your role.
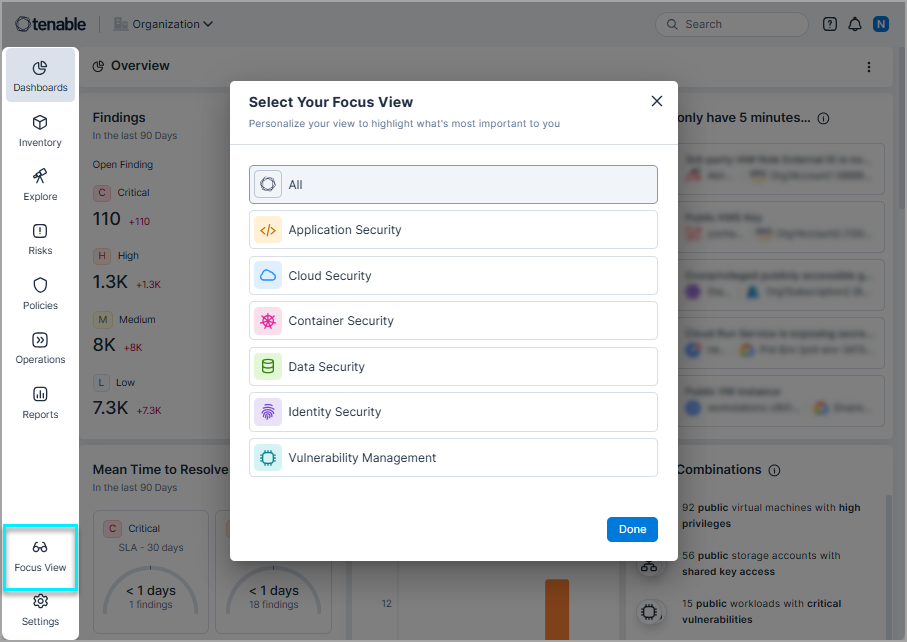
To select a focus area:
- Click your user profile icon at the top right and click Select Focus.
-
Select from one of the following focus areas:
Focus Area Description Relevant Roles All Displays all domains together for a unified view of your organization’s cloud security posture, including identities, data, workloads, and configurations All users who need a full cross-domain overview, such as security leads or CISOs Application Security Focuses on securing the software development lifecycle, from code to cloud, by identifying misconfigurations, secrets in code, and policy violations in IaC and CI/CD pipelines Application security engineers, DevSecOps engineer, cloud security architect Cloud Exposure Provides visibility into misconfigurations, compliance gaps, and risks across all cloud resources to strengthen overall cloud posture Cloud security architects, security platform engineers Container Security Highlights risks and misconfigurations in Kubernetes clusters and containerized workloads to ensure secure orchestration and deployment DevSecOps engineer, software security engineer Data Security Centers on discovering, classifying, and protecting sensitive data across cloud environments, reducing exposure and ensuring proper data boundaries Information security engineer, data security engineer Identity & Access Management Examines identities, roles, and permissions to answer “who can do what,” helping detect excessive privileges and high-risk access paths IAM engineer, Cloud security engineer, Security operations center (SOC) analyst Vulnerability Management Surfaces vulnerabilities across hosts, containers, and software to prioritize remediation and strengthen workload security Vulnerability management engineers, security risk analysts
In-Product Help
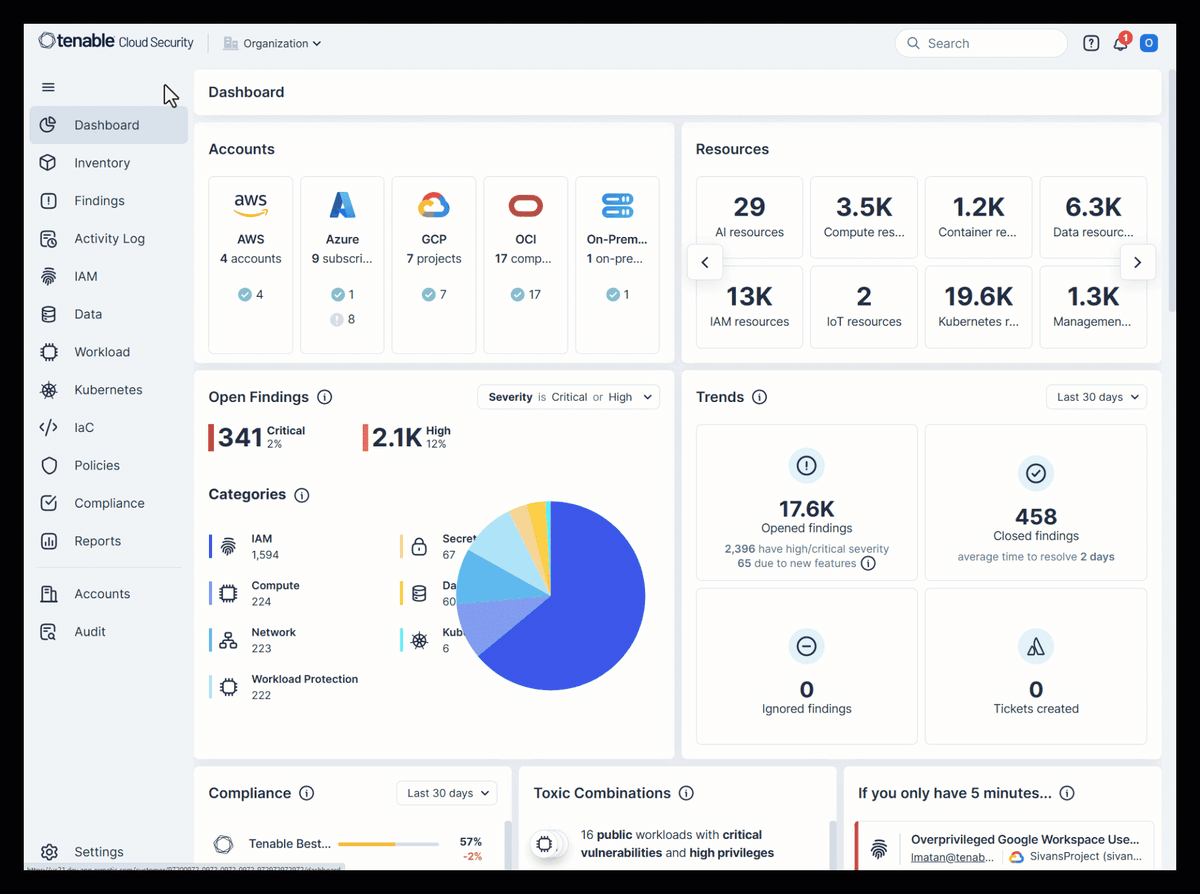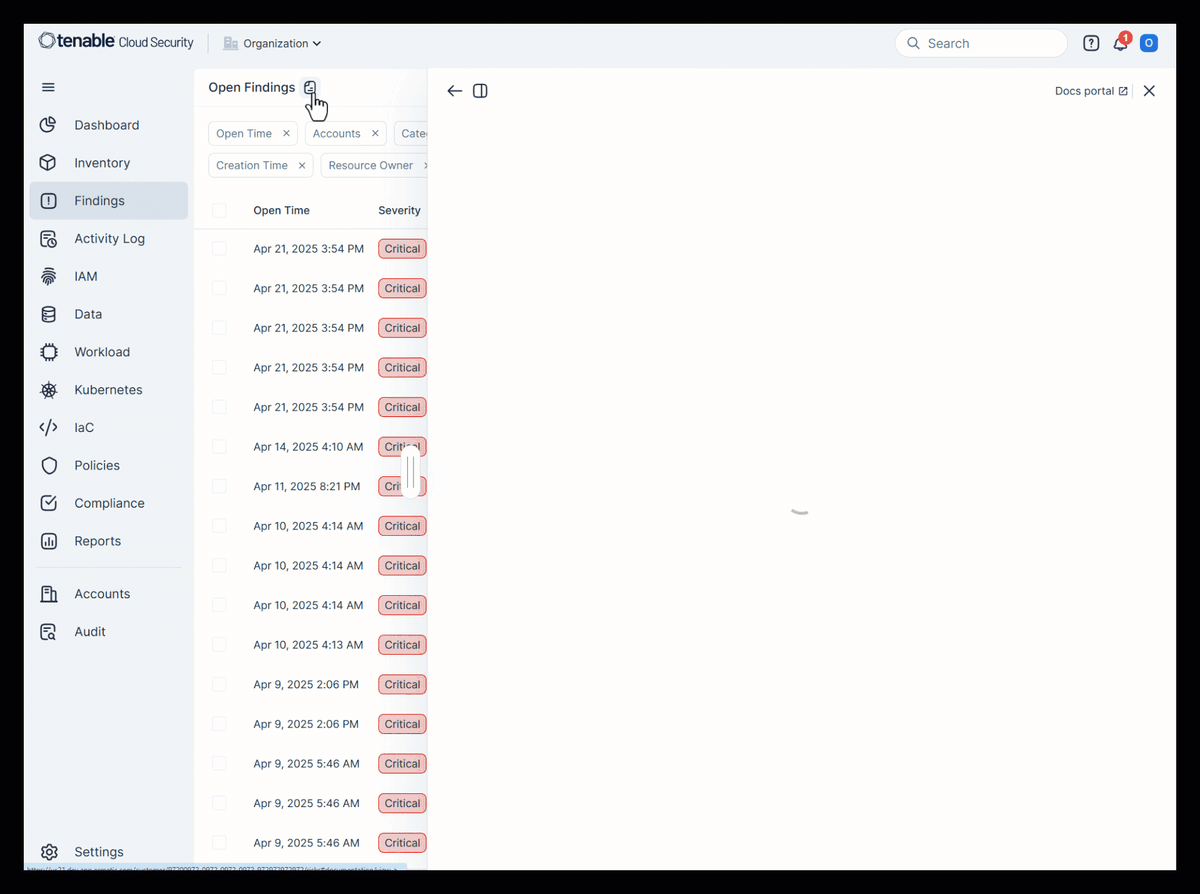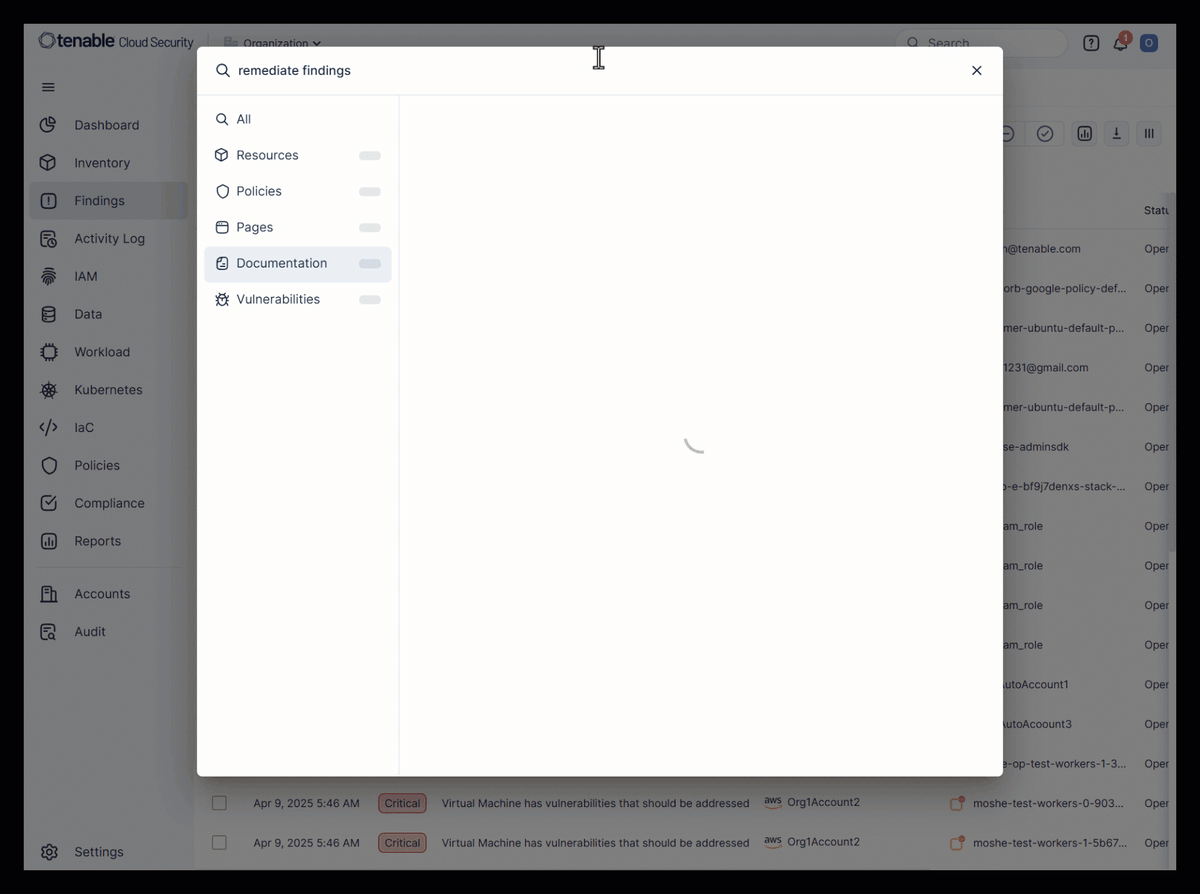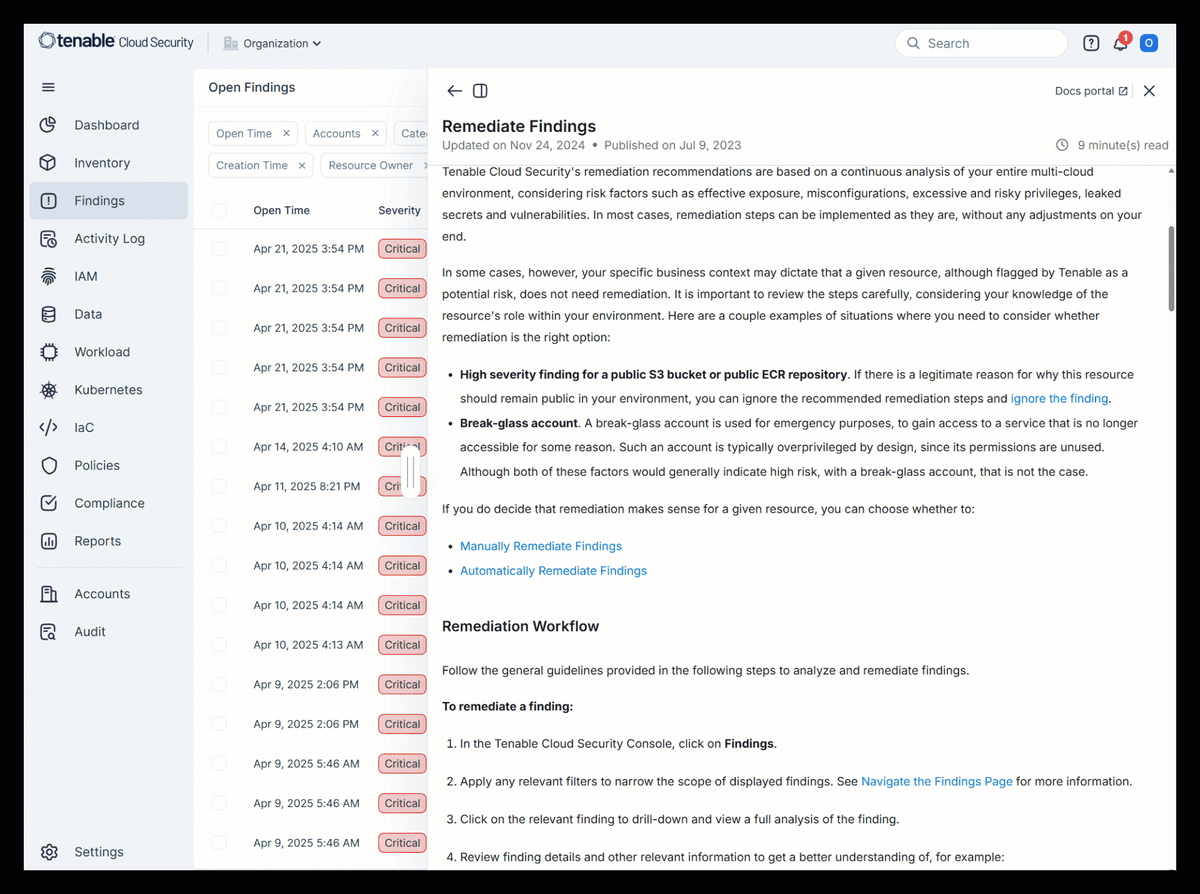
Access in-app help directly from the Console. Product documentation is accessible both via:
- Search
- Contextual help links
To access the full documentation site, click the Docs portal link at the top of the slideout panel.
Help Tools
Click the question mark icon at the top right of the Console to access various help tools.
- Release Notes — Descriptions of the latest features and improvements added to Cloud Exposure in the last release. Check this frequently for updates. See Release Notes.
- Documentation — Comprehensive product documentation that helps you find answers to your technical questions and learn how to use Cloud Exposure.
- API Explorer — Use GraphiQL, an in-browser tool, to write, validate, and test GraphQL queries. See API to learn more.
- Feedback — Submit feedback to the Cloud Exposure product team directly from the Console.
- Contact Us — See Contact Support.
User Profile
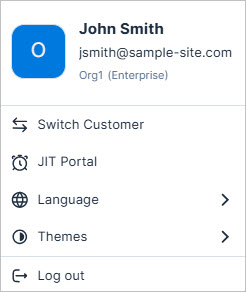
Click the icon at the top right of the Console to open your user profile. From here you can perform a variety of actions:
- See user details:
- User name / email address
- Company/organization name
- License type
- Customer ID. Used to register to the Tenable Community. See Contact Support for more information.
- Navigation:
- [JIT users only] Go to JIT Portal / Console. If you have access to both the Cloud Exposure Console and the JIT Portal, you can easily navigate back and forth between them.
- [Multi-tenant only] Switch Customer to view data for a different organization.
- Language
- English
- Japanese
- Themes
- Light Mode
- Dark Mode
- System
- Log out
Search across the Console
Use the global search to find resources (Inventory), vulnerabilities, policies, pages, and documentation across your environment, providing a single, streamlined way to navigate and find what you need.
- The search bar appears at the top right of the Cloud Exposure Console, regardless of which page you're on.
- Click Ctrl + K to access via keyboard shortcut.
- (Optional) Select a scope in the account scope dropdown to limit the search to a subset of accounts.
- Inventory results are divided by category (for example, Compute or IAM), across all clouds. For example, a search for "VM" could return results for AWS EC2 instances, Azure virtual machines, and GCP VM instances.
At-a-Glance Resource Profile View
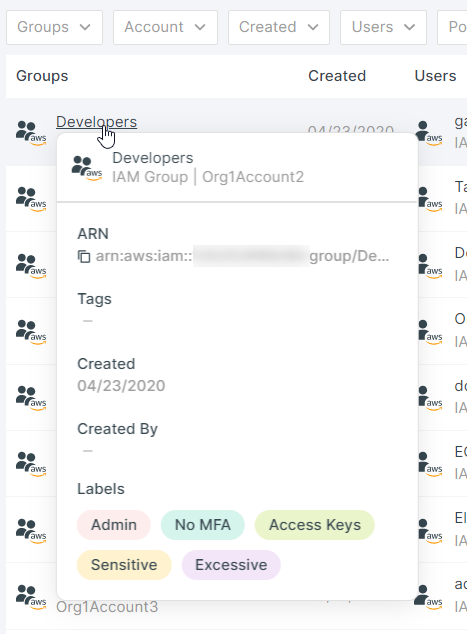
Hover over any resource name in the Inventory, access graph (permission mapping), Activity Log, or Findings page to see a mini profile view which contains a selection of the most important information about the resource. This allows you to learn more about the resource without having to context-switch by going to another page to see this information.
Color-Coded Risk Severity
Throughout the Console, different colors/icons are used to indicate the various risk severity levels that resources and findings pose to your organization. The following table maps these colors to their respective severity levels, and describes their implications within your cloud environment.
| COLOR | ICON | STATUS | DESCRIPTION | EXAMPLE |
|---|---|---|---|---|

|

|
Critical | Immediate action required | Administrative user with permissions to sensitive data, which aren't in use. |

|

|
High | Handle as soon as possible | Non-admin user with permissions to sensitive data, which aren't in use. |

|
|
Medium | Potential risk | User with permissions to sensitive resources such as bucket lists, but without permissions to read the bucket contents. |

|

|
Low | Monitor for escalation | User with limited use of assigned permissions. |
|
|
|
Informational | Useful information | A new GCP project was added to your organization. |

|
N/A | In Compliance (Compliance only) | No action necessary | No excessive permissions detected. Policy Rules and best practices met. |