Enable JIT Portal Login via SSO
Allow users to log in to the JIT Portal via SSO by establishing trust between your external identity provider (IdP) and Tenable One Cloud Exposure. This allows user provisioning by leveraging the existing corporate identities of your users.
Enable Login via AWS Identity Center (SAML 2.0)
Use AWS Identity Center as your identity provider (IdP) to enable login to the JIT Portal via SAML 2.0.
Before you begin:
-
Prerequisite: Authentication Domain The email domain used by your AWS Identity Center users must be added as an authentication domain in Cloud Exposure. If the domain is not configured, uploading the SAML metadata will fail during SSO setup.
To enable login to the JIT Portal using AWS Identity Center (SAML 2.0):
- In AWS, open AWS Identity Center.
- Navigate to Applications and click Add application.
- Select I have an application I want to set up, choose SAML 2.0, and then click Next.
- Under Configure application, enter a Display name and Description (for example, Enabling JIT Portal access via SSO for Cloud Exposure).
-
Under Application properties, enter the region-specific value of the Application start URL:
- Global (All regions): app.tenable.com/user
- United States Gov Cloud: app.tenable.us/user
-
Under Application metadata:
Enter the value of the Application ACS URL:
https://{URL}/api/console/authentication/saml2/user/acsWhere {URL} is:
- Global (All regions): app.tenable.com
- United States Gov Cloud: app.tenable.us
For Application SAML audience, enter:
urn:user.app.ermetic.comNote: The Application SAML Audience (also known as the Entity ID) uniquely identifies the JIT Portal as the service provider. This value is not region-specific.
- Click Submit to create the application.
-
Click Assign users and groups to assign any users or groups that should access the JIT Portal:
- From the search bar, add the relevant users or groups.
- Click Assign.
-
After the application is created, open it and select Actions > Edit attribute mappings:
Review or add the following attribute mappings*:
User Attribute in the Application Maps to This String Value or User
attribute in IAM Identity CenterFormat Subject (NameID) ${user:email} emailAddress http://schemas.xmlsoap.org/ws/2005/05/identity/claims/emailaddress ${user:email} unspecified http://schemas.xmlsoap.org/ws/2005/05/identity/claims/givenname ${user:givenName} unspecified http://schemas.xmlsoap.org/ws/2005/05/identity/claims/surname ${user:familyName} unspecified groups (optional) ${user:groups} unspecified *The groups attribute is case sensitive. Enter it exactly as shown if you plan to use AWS groups.
- Click Save changes.
- Still on the application page, select Actions > Edit configuration, and download the IAM Identity Center SAML metadata file.
- In the Cloud Exposure Console, navigate to Settings > Single Sign-On.
- Click Add Identity Provider and then select SAML.
- In the Choose Application drop-down, select JIT.
- Select File, upload the metadata file downloaded from AWS Identity Center, and click Add.
Enable Login via Google
Enable login to the JIT Portal via Google using one of the following identity specifications:
Enable Login via Google Using OIDC
To enable login using OIDC:
- In the Cloud Exposure Console, navigate to Settings > Single Sign-On.
- Click Add Identity Provider and then click Google.
-
In the Add Identity Provider dialog, click Add.
Note: Adding Google as an IdP in this way enables login to both the Cloud Exposure Console and the JIT Portal.
Enable Login via Google Using SAML
To enable login using SAML:
- In the Google Admin console, navigate to Apps > Web and mobile apps.
- Click Add app > Add custom SAML app.
- Enter an App name and then click CONTINUE.
- On the Google Identity Provider details page, click to DOWNLOAD METADATA.
- In the Cloud Exposure Console, navigate to Settings > Single Sign-On.
- Click Add Identity Provider and then click SAML.
- In the Add Identity Provider dialog, select JIT from the dropdown.
- Select File, upload the metadata that you downloaded from Google, and then click Add.
-
In the Google Admin console, on the Service provider details page, enter the following values for the respective fields:
- ACS URL: https://{region}.app.ermetic.com/api/authentication/saml2/user/acs
Where the value you enter for region depends on the value in the URL you use to log in to the Tenable One Cloud Exposure Console. See Product Security and Privacy.
- Entity ID: urn:user.app.ermetic.com
- Name ID format: EMAIL
- Name ID: Basic Information > Primary email
- Click CONTINUE.
-
On the Attribute mapping page, click ADD MAPPING, and then add the following attributes:
Google Directory Attributes to Mappings (App Attributes):
- First name — http://schemas.xmlsoap.org/ws/2005/05/identity/claims/givenname
- Last name — http://schemas.xmlsoap.org/ws/2005/05/identity/claims/surname
- Primary email — http://schemas.xmlsoap.org/ws/2005/05/identity/claims/emailaddress
- (Optional) Add support for Google groups.
- Click FINISH.
Enable Login via Microsoft Entra ID
Enable login to the JIT Portal via Microsoft Entra ID using one of the following identity specifications:
Enable Login via Microsoft Entra ID Using OIDC
To enable login using OIDC:
- In the Cloud Exposure Console, navigate to Settings > Single Sign-On.
- Click Add Identity Provider and then click Microsoft.
- In the Add Identity Provider dialog, grant access by clicking the link for JIT.
- Pick an account associated with the Cloud Exposure administrator in your organization.
-
Accept the requested permissions.
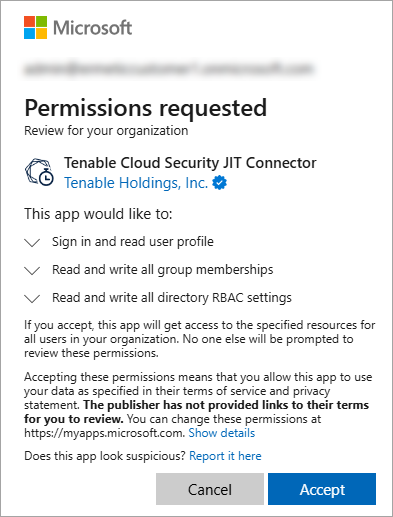
- Verify that I confirm that I granted access is selected, and click Add.
Enable Login via Microsoft Entra ID Using SAML
To enable login using SAML:
- In the Azure portal, navigate to Enterprise applications, and then add a New application.
- Click Create your own application, and then enter a name for the app.
- Select the default value of Integrate any other application you don’t find in the gallery (Non-Gallery) and then click Create.
- On the app Overview page that displays, in the Set up single sign on step, click Get started.
- Choose SAML as the SSO method.
-
Under Basic SAML Configuration, click Edit, and enter the following values for the respective fields:
- Identifier (Entity ID): urn:user.app.ermetic.com
- Reply URL (Assertion Consumer Service URL): https://app.tenable.com/api/authentication/saml2/user/acs
- Click Save.
-
Under Attributes & Claims, click Edit, and then, under Additional claims, delete the user.userprincipalname claim.
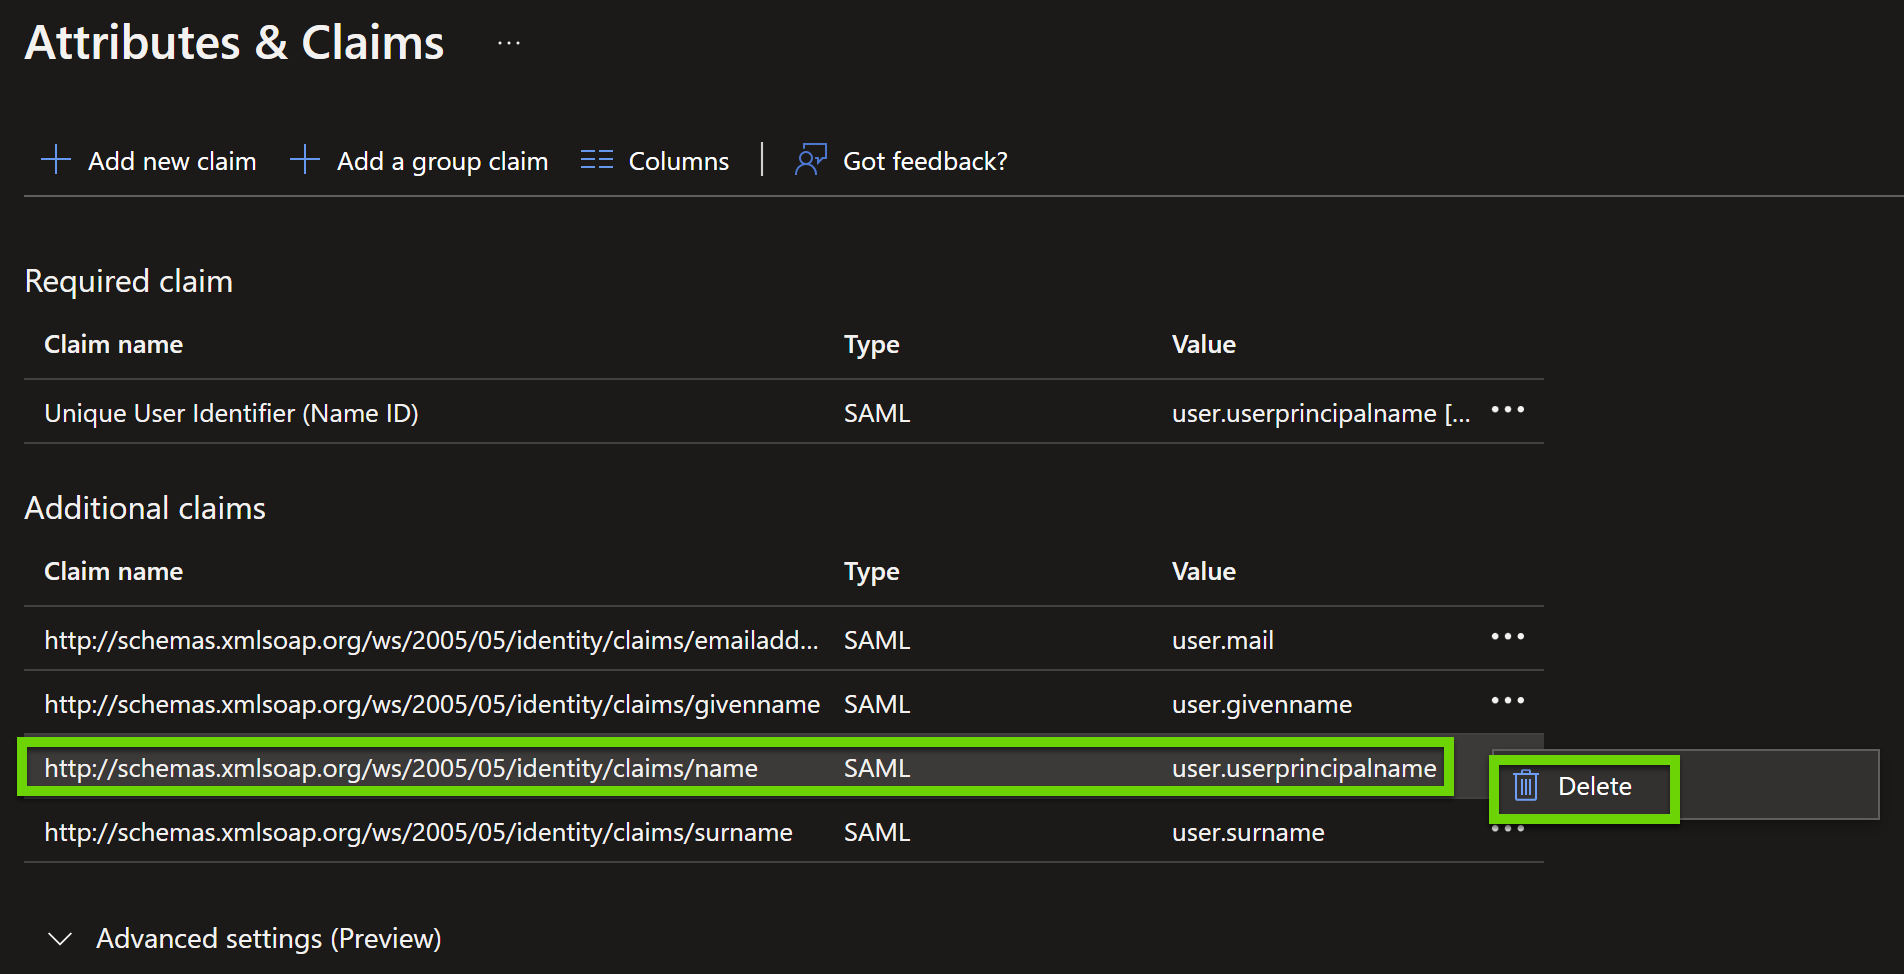
- Under SAML Certificates, click to download the Federation Metadata XML.
- In the Cloud Exposure Console, navigate to Settings > Single Sign-On.
- Click Add Identity Provider and then click SAML.
- In the Add Identity Provider dialog, select JIT from the dropdown.
- Select File, upload the metadata that you downloaded from Azure, and then click Add.
Enable Login via Okta
Enable login to the JIT Portal via Okta by leveraging the SAML 2.0 identity specification.
To enable login to the JIT Portal via Okta:
- In the Okta Admin Console, navigate to Applications > Applications.
- Click Browse App Catalog.
- Enter Cloud Exposure JIT in the Search field, click the application tile, and then click Add.
- Select the Sign On tab in the app, and then click Edit.
-
Scroll to Advanced Sign-on Settings and enter a Region, where the value you enter depends on the value in the URL you use to log in to the JIT Portal (https://{region}.app.ermetic.com/user/).
See Product Security and Privacy for details.
- In the SAML Setup section, click View SAML setup instructions.
- Under Configuration Steps, copy the URL value listed in step 2.
- In the Cloud Exposure Console, navigate to Settings > Single Sign-On.
- Click Add Identity Provider and then click SAML.
- In the Add Identity Provider dialog, select JIT from the dropdown.
- Select URL, paste the URL value from Okta, and then click Add.
Enable Login via OneLogin
Enable login to the JIT Portal via OneLogin by leveraging the SAML 2.0 identity specification.
To enable login to the JIT Portal via OneLogin:
- In the OneLogin Admin Console navigate to Applications > Applications.
- Click Add App.
- Search for and select SAML Custom Connector (Advanced).
- In the Configuration page, enter a Display Name (For example, 'Cloud Exposure'). and then click Save.
-
Navigate to the Configuration tab, and enter the following values for these application details:
- Audience (EntityID): urn:user.app.ermetic.com
- ACS (Consumer) URL Validator / ACS (Consumer) URL: https://{region}.app.ermetic.com/api/authentication/saml2/user/acs
Where the value you enter for region depends on the value in the URL you use to log in to the Tenable One Cloud Exposure Console. See Product Security and Privacy.
-
Navigate to the Parameters tab, and click
 to add the following new fields/values:
Field name to Value:- http://schemas.xmlsoap.org/ws/2005/05/identity/claims/emailaddress — Email
- http://schemas.xmlsoap.org/ws/2005/05/identity/claims/givenname — First Name
- http://schemas.xmlsoap.org/ws/2005/05/identity/claims/surname — Last Name
Important: Make sure to enable the Include in SAML assertion flag for each field/value.Note: The NameID value field appears out-of-the-box in OneLogin. You can leave this field as is.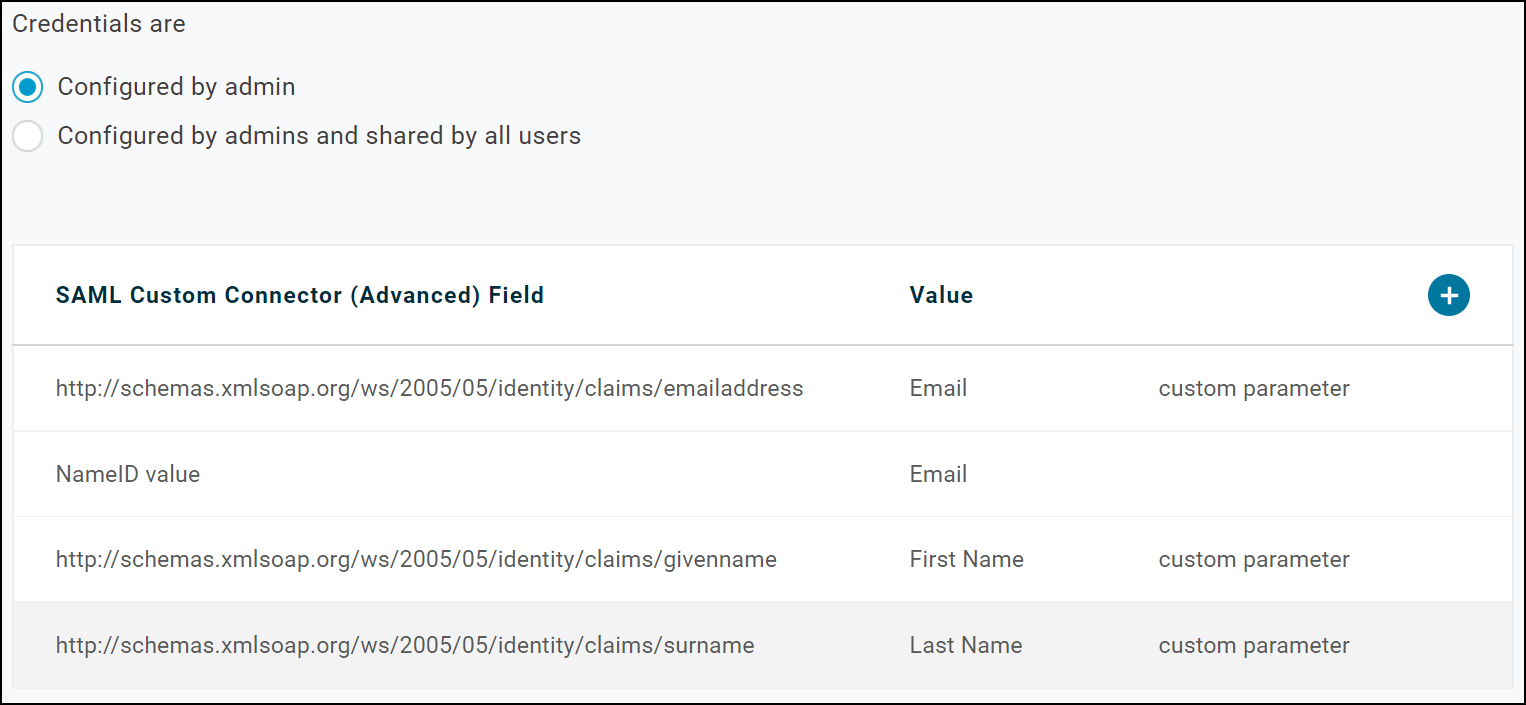
- Navigate to the SSO tab and set the SAML Signature Algorithm to SHA-256.
- Click on the More Actions dropdown and select SAML Metadata. Copy the metadata.
- In the Cloud Exposure Console, navigate to Settings > Single Sign-On.
- Click Add Identity Provider and then click SAML.
- In the Add Identity Provider dialog, select JIT from the dropdown.
- Select File, upload the metadata you copied from OneLogin, and then click Add.
Enable Login via Ping Identity
Enable login to the JIT Portal via Ping Identity by leveraging the SAML 2.0 identity specification.
To enable login to the JIT Portal via Ping Identity:
- In the Ping Identity Admin Console, navigate to Connections > Applications.
- Click
 to add an application.
- Enter an Application Name. For example, ‘Cloud Exposure’.
- Choose SAML Application as the Application Type and then click Configure.
-
Under SAML Configuration, choose Manually Enter and then enter the following details:
ACS URL — https://{region}.app.ermetic.com/api/authentication/saml2/user/acs
Where the value you enter for region depends on the value in the URL you use to log in to the Tenable One Cloud Exposure Console. See Product Security and Privacy.
- Entity ID — urn:user.app.ermetic.com
- Click Save.
-
Navigate to the Attribute Mappings tab, click Edit
 and then add the following attributes:
Attributes to PingOne Mappings:
- http://schemas.xmlsoap.org/ws/2005/05/identity/claims/emailaddress — Email Address
- http://schemas.xmlsoap.org/ws/2005/05/identity/claims/givenname — Given Name
- http://schemas.xmlsoap.org/ws/2005/05/identity/claims/surname — Family Name
-
Click the radio button to enable the App.
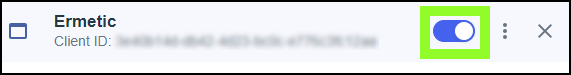
- Navigate to the Configuration tab and click Download Metadata.
- In the Cloud Exposure Console, navigate to Settings > Single Sign-On.
- Click Add Identity Provider and then click SAML.
- In the Add Identity Provider dialog, select JIT from the dropdown.
- Select File, upload the metadata you copied from OneLogin, and then click Add.
Enable Login via Custom SAML 2.0 Provider
If you work with a provider other than one of those documented in the sections above, you can enable login to the JIT Portal via that provider by leveraging the SAML 2.0 identity specification.
To enable login to the JIT Portal via a custom SAML provider:
- Follow the steps outlined by the relevant provider to add a dedicated application for Cloud Exposure. Consult with any relevant documentation, if needed.
-
In the application, configure the following SAML details:
- Entity ID: urn:user.app.ermetic.com
ACS (Redirect URL): https://{region}.app.ermetic.com/api/authentication/saml2/user/acs
Where the value you enter for region depends on the value in the URL you use to log in to the Tenable One Cloud Exposure Console. See Product Security and Privacy.
- Encryption: SHA-256
- SAML NameID Format: Email
-
Add the following SAML attributes, mapping them, as relevant, to the given provider:
Attributes to Mappings:
- Email Address: http://schemas.xmlsoap.org/ws/2005/05/identity/claims/emailaddress
- Given Name: http://schemas.xmlsoap.org/ws/2005/05/identity/claims/givenname
- Family Name: http://schemas.xmlsoap.org/ws/2005/05/identity/claims/surname
Note: Name Format = unspecified - Download the metadata.
- In the Cloud Exposure Console, navigate to Settings > Single Sign-On.
- Click Add Identity Provider and then click SAML.
- In the Add Identity Provider dialog, select JIT from the dropdown.
- Select File, upload the metadata that you downloaded earlier, and then click Add.