JIT Personas and Workflow
The JIT access workflow involves the participation of the following personas:
- Administrator — A Tenable One Cloud Exposure user (Administrator or JIT Administrator role) who manages eligibilities via the JIT Portal and can audit JIT-related activity.
- Requester — A user or group member in your cloud environment who wants to access accounts, and submits a request via the self-service JIT Portal, via Slack, or via Teams.
- Approver — A user or group member in your cloud environment who has been designated in an eligibility to manually review/approve requests via the self-service JIT Portal, via Slack, or via Teams.
JIT Workflow
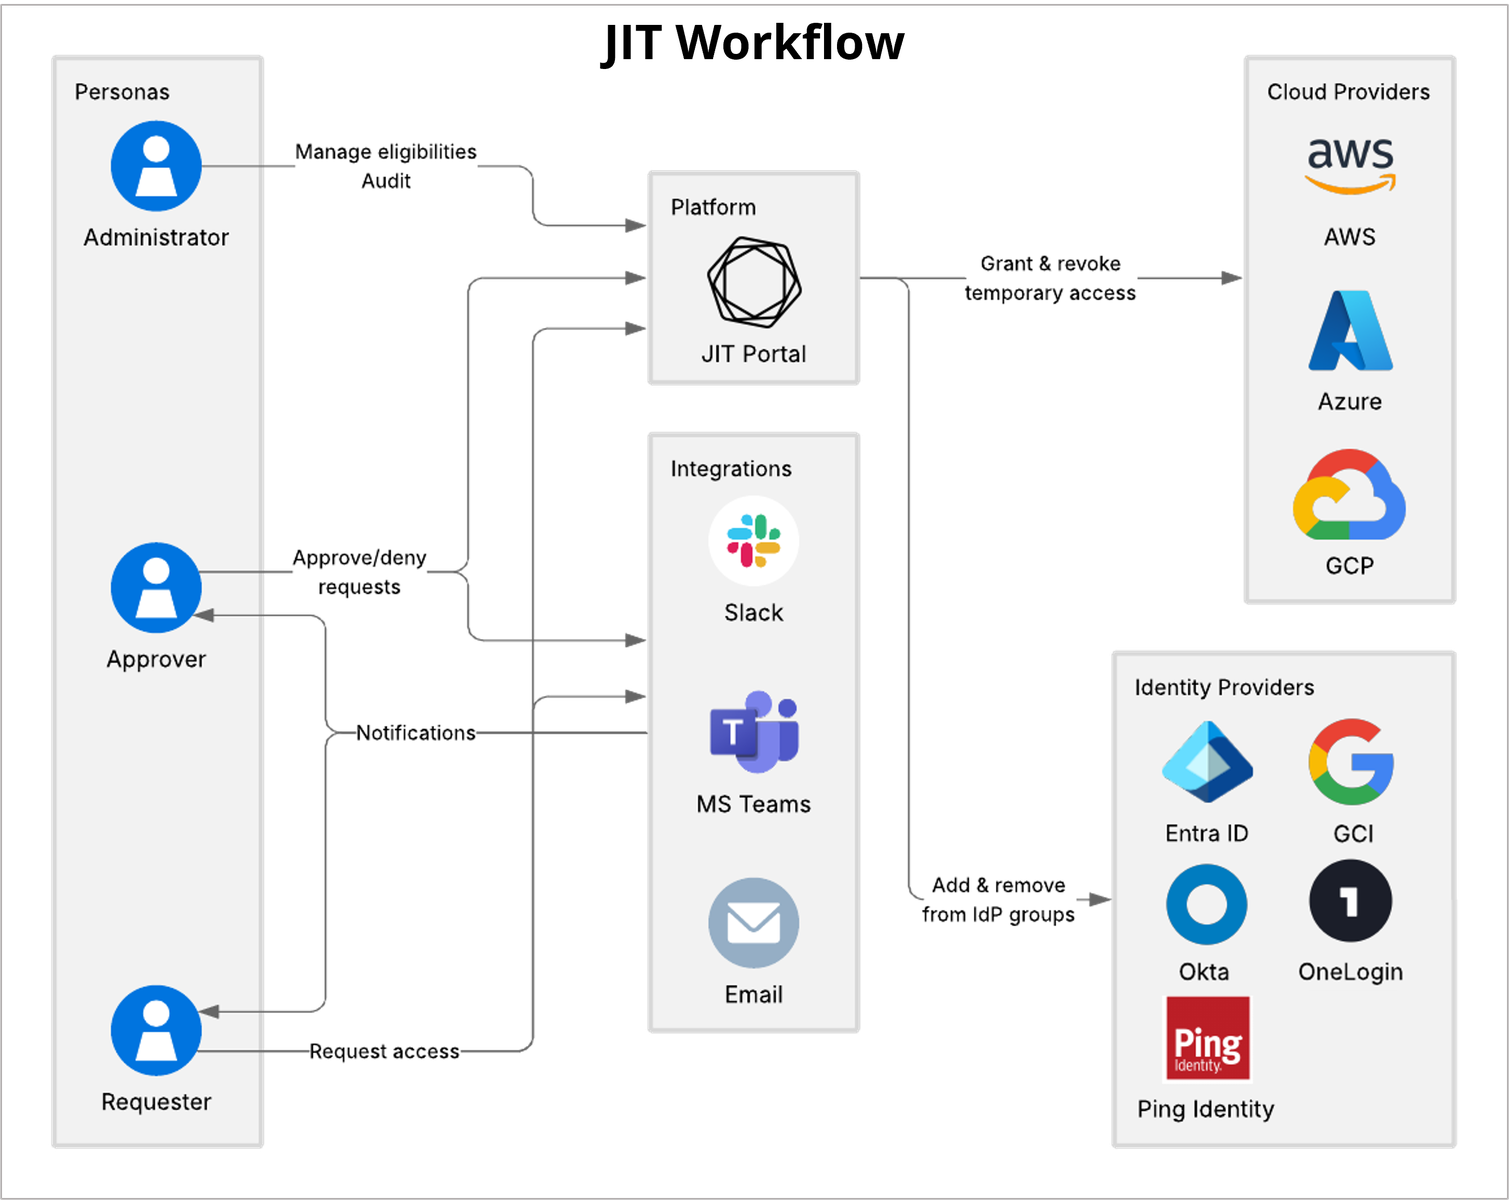
- An administrator adds an eligibility, which is a predefined policy that states who can request access and what they can request (account scope/permissions/duration). The policy also defines whether access is approved and granted automatically, or whether it must wait for an explicit approval.
- A requester, who has been included in an eligibility, requests access to an account. The user’s ability to request access is based on the eligibility criteria defined by the administrator.
- If the eligibility criteria stipulates automatic approval, the access request is approved and granted immediately.
- If the eligibility criteria requires explicit approval, the request is pending, and an email notification/Slack/Teams message (if enabled) is sent to the approvers. Optionally, you can also define additional email addresses or Slack/Teams channels to receive notifications.
- An approver reviews the request, and decides whether to approve or deny.
-
When an approver approves the request:
- The requester is granted access to the account for a specific period of time using the defined permission level. If there are multiple approvers on the same level in the approval workflow, only one of them needs to grant approval.
- If you configured a multi-level approval workflow, a notification is sent to the second- or third-level approver for review. Access is only granted to the requester after the final approver defined in the eligibility approves the request.
- After the duration of the entitlement has expired, the requester’s access is automatically revoked.