Semperis Connector
The following is not supported in Tenable FedRAMP Moderate environments. For more information, see the Tenable FedRAMP Product Offering.
Semperis Lightning is an identity security platform that monitors Active Directory and Microsoft Entra ID for misconfigurations, excessive privileges, stale accounts, and weak authentication settings. Semperis Lightning reports these risks as Indicators of Exposure (IoEs).
The following steps allow you to configure this connector for use with Tenable Exposure Management from start to finish.
Connector Details
Tenable Exposure Management ingests Semperis Lightning identity objects as assets, and each Indicator of Exposure that an identity object fails as a misconfiguration finding.
| Details | Description |
|---|---|
|
Supported products |
Semperis Lightning (cloud) for Active Directory and Microsoft Entra ID Available in the North America and Europe regions. |
|
Category |
Identity Security |
| Ingested data | Assets and Findings |
|
Ingested Asset Classes |
Account Group Role |
|
Integration type |
UNI directional (data is transferred from the connector to Tenable Exposure Management in one direction) |
|
Supported version and type |
Semperis Lightning (cloud), External API v1 |
Prerequisites and User Permissions
Before you begin configuring the connector, make sure to:
-
Confirm that you have an active Semperis Lightning tenant.
Generate a Semperis Lightning API key
The Semperis role attached to the API key must grant read access to your inventory objects, indicator executions, indicator result objects, and Indicator of Exposure definitions. The lightest built-in role that covers all four is enough. Semperis recommends the OrganizationOwner role for API access, and a read-only equivalent also works when it exposes those four areas.
-
Log in to Semperis Lightning.
-
In the upper-right corner, click your account, and then click Access tokens.
-
Create a new API key. Type a name that identifies Tenable, so that you can rotate the key later, and set an expiration date.
-
Copy the generated key to a safe location. You need it to configure the connector.
Note: Semperis Lightning shows the key only once.
Add a Connector
To add a new connector:
-
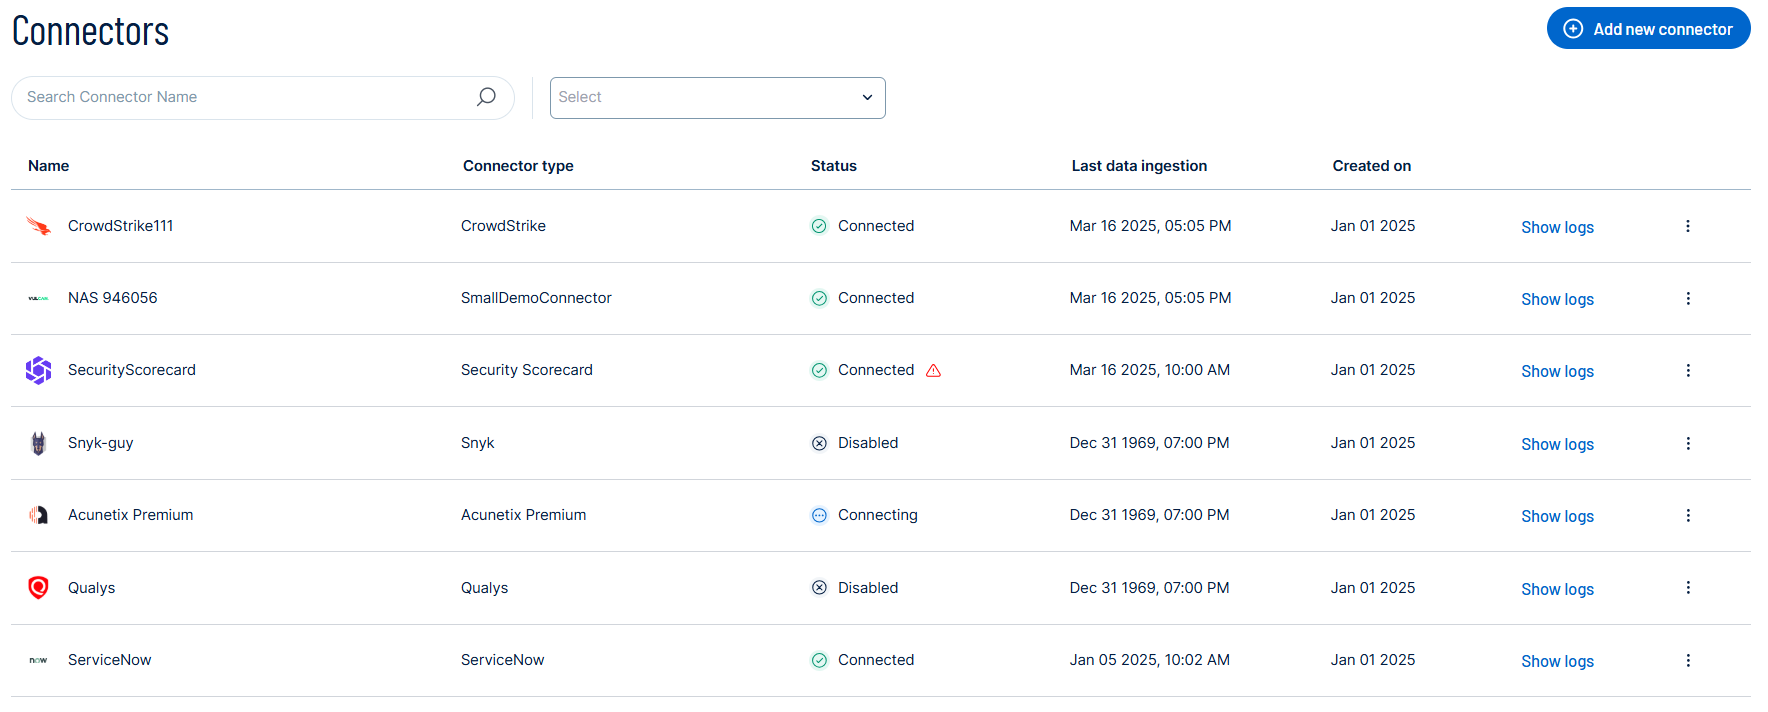
In the left navigation menu, click Connectors.
The Connectors page appears.
-
In the upper-right corner, click
 Add new connector.
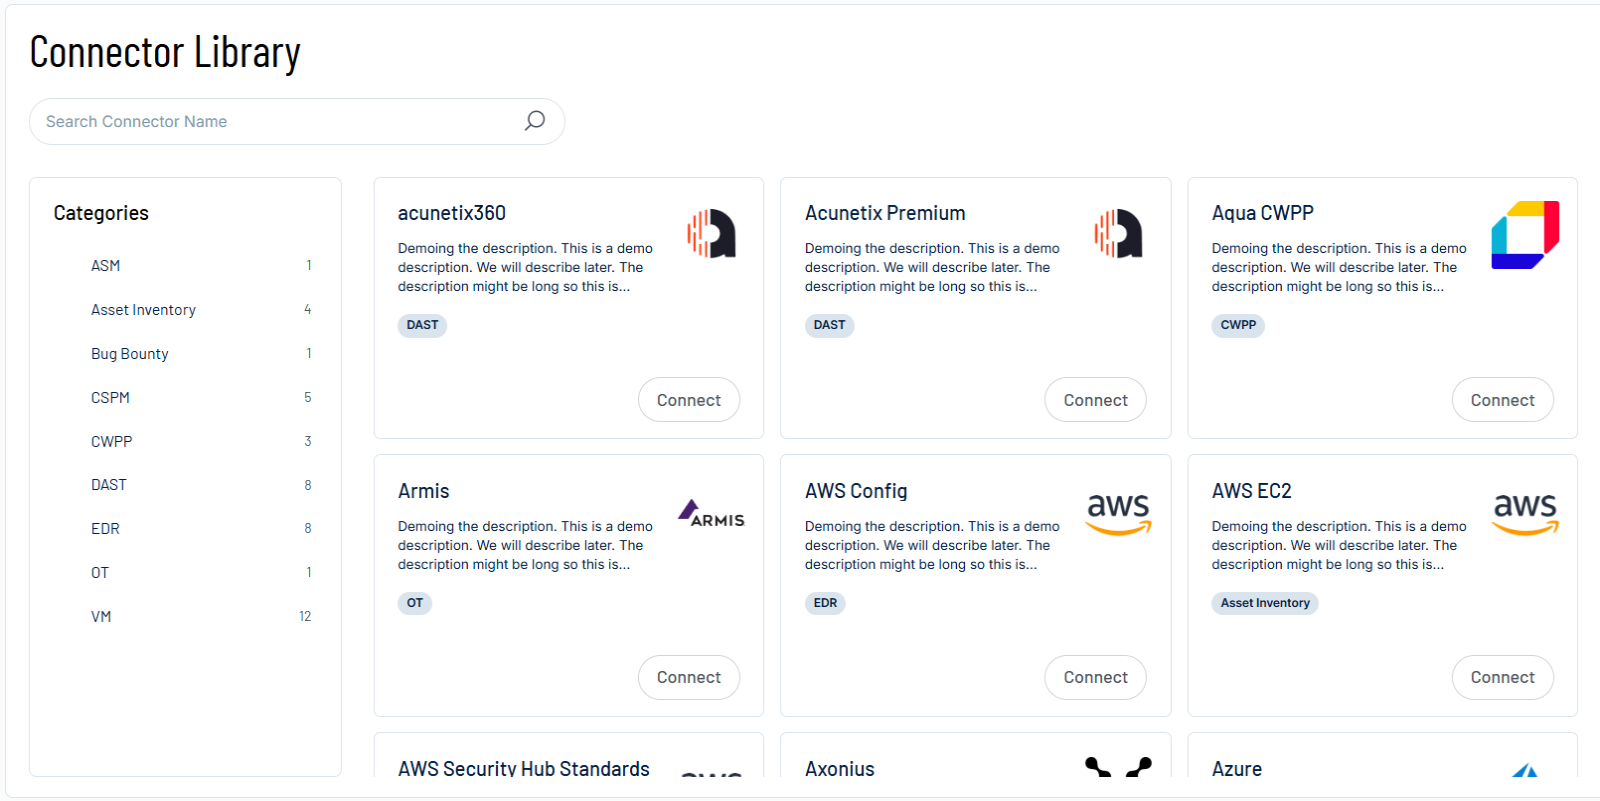
The Connector Library page appears.
-
In the search box, type the name of the connector.
-
On the tile for the connector, click Connect.
The connector configuration options appear.
Configure the Connector
To configure the connector:
-
(Optional) In the Connector's Name text box, type a descriptive name for the connector.
-
(Optional) To use a preconfigured on-prem connector to connect to this connector, from the Gateway drop-down, select the on-prem connector you want to use for the connector. Otherwise, select Don't use gateway.
Note: For information about configuring a gateway, see Tenable On-Prem Connector. -
From the Base URL drop-down, select the region that hosts your Semperis Lightning tenant.
-
In the API Key text box, type the Semperis Lightning API key that you generated.
-
Data pulling configuration: This configuration has dynamic settings tailored to the specific connector and integration type. Below are the configurations relevant to this connector.
-
In the Asset Retention text box, type the number of days after which you want assets to be removed from Tenable Exposure Management. If an asset has not been detected or updated within the specified number of days, it is automatically removed from the application, ensuring your asset inventory is current and relevant.
Tip: For more information, see Asset Retention.
-
-
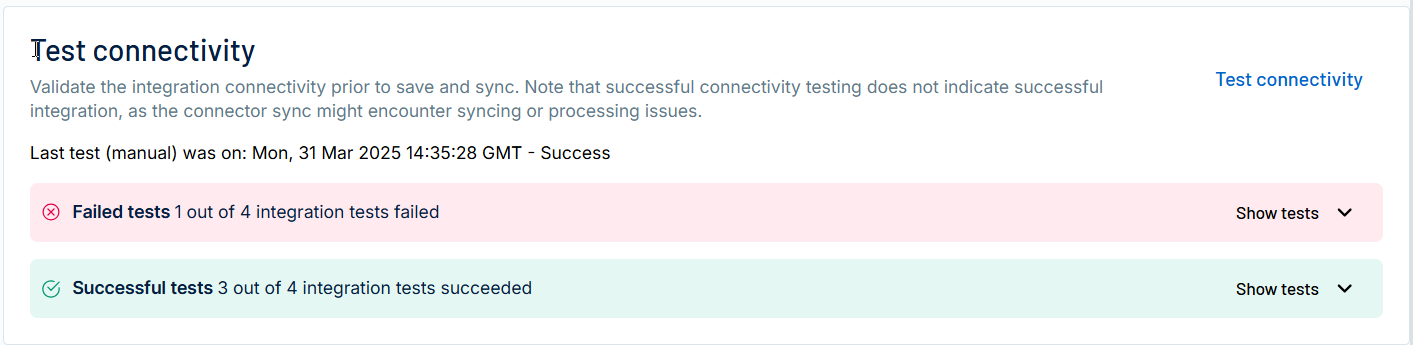
In the Test connectivity section, click the Test Connectivity button to verify that Tenable Exposure Management can connect to your connector instance.
-
A successful connectivity test confirms that the platform can connect to the connector instance. It does not, however, guarantee that the synchronization process will succeed, as additional syncing or processing issues may arise.
-
If the connectivity test fails, an error message with details about the issue appears. Click Show tests for more information about the exact error.
-
-
In the Connector scheduling section, configure the time and day(s) on which you want connector syncs to occur.
Tip: For more information, see Connector Scheduling. -
Click Create & Sync. Tenable Exposure Management begins syncing the connector. The sync can take some time to complete.
-
To confirm the sync is complete, do the following:
-
Navigate to the Connectors page and monitor the connector's status. Sync is complete once the connector status is Connected.
-
View the sync logs for the connector to monitor the logs for a successful connection.
-
Semperis in Tenable Exposure Management
Locate Connector Assets in Tenable Exposure Management
As the connector discovers assets, Tenable Exposure Management ingests those devices for reporting.
To view assets by connector:
-
In Tenable Exposure Management, navigate to the Assets page.
-
In the Filters section, under 3rd Party Connectors, click the connector name for which you want to view assets.

The asset list updates to show only assets from the selected connector.
-
Click on any asset to view Asset Details.
Locate Connector Weaknesses in Tenable Exposure Management
As the connector discovers weaknesses, Tenable Exposure Management ingests those weaknesses for reporting.
To view weaknesses by connector:
-
In Tenable Exposure Management, navigate to the Weaknesses page.
-
In the Filters section, under 3rd Party Connectors, click the connector name for which you want to view weaknesses.
The weaknesses list updates to show only weaknesses from the selected connector.
-
Click on any weakness to view Weakness Details.
Locate Connector Findings in Tenable Exposure Management
As the connector discovers individual findings, Tenable Exposure Management ingests those findings for reporting.
To view findings by connector:
-
In Tenable Exposure Management, navigate to the Findings page.
-
In the Filters section, under 3rd Party Connectors, click the connector name for which you want to view findings.
The findings list updates to show only assets from the selected connector.
-
Click on any asset to view Finding Details.
Data Mapping
Tenable Exposure Management integrates with the connector via API to retrieve relevant weakness and asset data, which is then mapped into the Tenable Exposure Management system. The following tables outline how fields and their values are mapped from the connector to Tenable Exposure Management.
Semperis Lightning returns every identity object through a single inventory call. Tenable Exposure Management routes each object to the Account, Group, or Role asset class according to its identity type. The following table shows how identity types map to asset classes.
|
Tenable Exposure Management Asset Class |
Semperis Identity Type |
|---|---|
|
Account |
User Computer Device ServicePrincipal GroupManagedServiceAccount ForeignSecurityPrincipal Application |
|
Group |
Group |
|
Role |
DirectoryRole |
Account Mapping
| Tenable Exposure Management UI Field |
Semperis Field |
|---|---|
|
Asset Name Account Name |
DisplayName |
| Asset Provider ID | ObjectId |
| AD Object GUID | ObjectId (Active Directory identities only) |
| External Identifier | ObjectId (Microsoft Entra ID identities only) |
| Account Type | IdentityType |
| Provider Names | DirectoryType |
| AD Object SID | oid (Active Directory identities only) |
| AD Distinguished Name | DistinguishedName (Active Directory identities only) |
| AD Forest Name | directory.friendlyName |
| Account Login | UserPrincipalName (Active Directory identities only) |
| Asset Custom Attributes |
UPN In Zone |
Note: For Microsoft Entra ID identities, the user principal name is ingested as the UPN custom attribute rather than as Account Login.
Group Mapping
| Tenable Exposure Management UI Field |
Semperis Field |
|---|---|
|
Asset Name Group Name |
DisplayName |
| Asset Provider ID | ObjectId |
| AD Object GUID | ObjectId (Active Directory identities only) |
| External Identifier | ObjectId (Microsoft Entra ID identities only) |
| Provider Names | DirectoryType |
| AD Object SID | oid (Active Directory identities only) |
| AD Distinguished Name | DistinguishedName (Active Directory identities only) |
| AD Forest Name | directory.friendlyName |
| Group Is Privileged | Zone |
| Asset Custom Attributes | In Zone |
Role Mapping
| Tenable Exposure Management UI Field |
Semperis Field |
|---|---|
|
Asset Name Role Name |
DisplayName |
| Asset Provider ID | ObjectId |
| External Identifier | ObjectId |
| Provider Names | MICROSOFT_ENTRA_ID |
| Asset Custom Attributes | In Zone |
Note: Semperis Lightning reports directory roles for Microsoft Entra ID only.
Finding Mapping
| Tenable Exposure Management UI Field |
Semperis Field |
|---|---|
| Finding Name | Name |
| Description | Description |
| Finding Type | MISCONFIGURATION |
| Severity | SeverityLevel |
| Score | Weight |
| Solution | Remediation |
| Last seen (Observed) | IndicatorExecution.endTime |
| State | ResultStatus |
| Finding Custom Attributes |
Category Last Run Score Security Framework Tags |
Note: Semperis Lightning does not report vulnerabilities that carry a Common Vulnerabilities and Exposures (CVE) identifier. Every Indicator of Exposure becomes a misconfiguration finding, and the severity comes from the Indicator of Exposure definition rather than from a score calculated for each identity object.
Finding Status Mapping
|
Tenable Exposure Management Status |
Semperis Status |
|---|---|
|
Active |
Failed — the Indicator of Exposure check did not pass for this identity object. |
|
Fixed |
Passed — the Indicator of Exposure check now passes for this identity object. |
Finding Severity Mapping
|
Tenable Exposure Management Severity |
Semperis Severity |
|---|---|
|
Critical |
critical |
|
High |
high |
|
Medium |
medium |
|
Low |
low |
|
None |
info, or any other value |
Note: Tenable derives the finding severity from the SeverityLevel value on the Indicator of Exposure definition. The connector also ingests the Semperis Weight value, a number from 1 to 10, as the finding score.
Status Update Mechanisms
Every day, Tenable Exposure Management syncs with the vendor's platform to receive updates on existing findings and assets and to retrieve new ones (if any were added).
The table below describes how the status update mechanism works in the connector for findings and assets ingested into Tenable Exposure Management.
|
Update Type in Tenable Exposure Management |
Mechanism (When?) |
|---|---|
|
Archiving Assets |
|
|
Change a Finding status from "Active" to "Fixed" |
|
Uniqueness Criteria
Tenable Exposure Management uses defined uniqueness criteria to determine whether an ingested asset or finding should be recognized as a distinct record. These criteria help define how assets and findings are identified and counted from each connector.
Tip: For more information, see Asset Deduplication in Tenable Exposure Management
The uniqueness criteria for this connector are as follows:
|
Data |
Uniqueness Criteria |
|---|---|
|
Asset |
ObjectId (uniquely identifies the identity object, and is stable across syncs) |
|
Vulnerability |
IndicatorId (uniquely identifies the Indicator of Exposure definition) |
|
Finding |
ObjectId + IndicatorId (uniquely identifies one affected identity object per indicator run) |
Support Limitations and Expected Behavior
This section outlines any irregularities, expected behaviors, or limitations related to integration of the connector and Tenable Exposure Management. It also highlights details about ingested and non-ingested data to clarify data handling and functionality within this integration.
-
Semperis Lightning does not report vulnerabilities that carry a Common Vulnerabilities and Exposures (CVE) identifier. Every finding is a misconfiguration.
-
The connector ingests only the identity types listed in the asset class table. Organizational units, administrative units, group policy containers, domain DNS zones, generic containers, built-in domains, and session data are not ingested.
-
An identity object that Semperis Lightning returns without an ObjectId value has no unique key, and the connector does not ingest it.
-
Semperis Lightning caps the size of the affected-objects response for each indicator run. An Indicator of Exposure that affects a very large number of identity objects can return a truncated list, and the findings for the objects beyond the cap do not reach Tenable Exposure Management.
-
Semperis Lightning does not currently expose the account status, multifactor authentication (MFA) status, last updated date, Security Accounts Manager (SAM) account name, built-in role flag, or the date an Indicator of Exposure was first detected against an identity object. These fields are not ingested.
API Endpoints in Use
API version: Semperis Lightning External API v1.
|
API |
Use in Tenable Exposure Management |
Permissions required |
|---|---|---|
|
|
Exchanges the API key for a short-lived token used on all other calls. |
API key with tenant read access |
|
|
Fetches identity objects and maps the in-scope identity types to assets. |
Read on inventory |
|
|
Lists the most recent Indicator of Exposure runs and determines which indicators to expand. |
Read on indicators |
|
|
Fetches the identity objects affected by each indicator run and maps them to findings. |
Read on indicator results |
|
|
Fetches the Indicator of Exposure definitions that enrich the finding name, description, severity, weight, and remediation guidance. |
Read on IoE definitions |
Data Validation
This section shows how to validate and compare data between Tenable Exposure Management and Semperis Lightning.
Asset Data Validation
Objective: Ensure the number of identity objects in a Semperis Lightning directory aligns with the number of assets displayed in Tenable Exposure Management.
In Semperis Lightning:
-
Go to Inventory > Identities.
-
Note the number of identity objects in the directory whose identity type the connector ingests.
In Tenable Exposure Management:
-
Locate your connector assets, filtered by Source = Semperis.
-
Group the assets by asset class to compare the Account, Group, and Role counts separately.
-
Compare the total number of assets between Semperis Lightning and Tenable Exposure Management.
Expected outcome: The total numbers should be close, but they do not always match exactly. The Semperis Lightning inventory can include identity types that the connector does not ingest, and new identity objects can appear between the last completed sync and the moment you compare the two screens.
If an asset is not visible in Tenable Exposure Management, check the following conditions:
-
The identity type is one of the types listed in the asset class table.
-
The identity object has an ObjectId value.
-
The connector's last sync completed successfully.
-
The asset was archived because it did not return in the connector's last sync.
Tip: To learn more on how assets are archived and findings change status, see Status Update Mechanisms.
Finding Data Validation
Objective: Ensure the number of Indicators of Exposure in a Semperis Lightning directory aligns with the number of findings in Tenable Exposure Management.
In Semperis Lightning:
-
Open the directory's Exposures page, and then select the IOE Found tab.
-
Note the number of rows on the tab. Each row is one Indicator of Exposure that the directory currently fails, together with its own affected-objects count.
In Tenable Exposure Management:
-
Locate your connector findings, filtered by Source = Semperis and State = Active.
-
Compare the number of distinct findings with the number of rows on the IOE Found tab.
-
To check a single finding, open it and compare the number of linked assets with the affected-objects value that Semperis Lightning shows for the same Indicator of Exposure.
Expected outcome: Each Indicator of Exposure becomes exactly one finding, so the two counts should match. When you compare the affected-objects value, read only the leading number, because Semperis Lightning appends the number of objects that it excludes from scoring.
If a finding is missing from Tenable Exposure Management or no longer active, check the following conditions:
-
The most recent run of the Indicator of Exposure found at least one affected identity object.
-
The affected identity object has an ObjectId value.
-
The affected-objects response was not truncated by the Semperis Lightning response cap. An Indicator of Exposure that affects a very large number of identity objects can drop the object from the list.
-
The finding is marked as Fixed and appears under the Fixed state on the Findings screen.
Tip: To learn more on how assets are archived and findings change status, see Status Update Mechanisms.